TISAX software that builds your evidence base automatically
Docusnap365 inventories your IT infrastructure, links risks to real systems and delivers the evidence base for your TISAX assessment.
TISAX Assessment: Information Security as a Supplier Criterion
TISAX software maps the assessment requirements of the VDA ISA catalogue onto a single platform. IT infrastructure is inventoried automatically, risks assessed against discovered systems, access rights analysed and policies maintained as controlled documents. The evidence base grows from one shared data foundation rather than from collated spreadsheets and file shares. The TISAX assessment scheme builds on ISO 27001.
OEMs and Tier-1 partners require a TISAX label before they award contracts or share confidential design data. The requirements go well beyond a one-off audit: the VDA ISA catalogue calls for up-to-date documentation, a traceable link between risks, measures and responsibilities, and evidence that your organisation maintains these structures over time.
Why Assessment Preparation Takes So Much Time
Most companies already have the data an assessment requires. The challenge is pulling it together in one place before the assessor arrives.
Scattered Documentation
Network diagrams live in Visio, permissions in Excel, policies on a file server. That setup works day to day. The moment an assessor asks for the full picture, the manual gathering begins.
Risk Registers Without Substance
A risk register kept in a separate spreadsheet describes risks without tying them to a specific system. In an assessment, that is rarely enough: assessors want to see which asset is affected, who owns the measure and by when.
Outdated Asset Records
Months can pass between the last manual update and the assessment date. Devices are added, configurations change, access rights grow. What was meant to be the current state ends up describing yesterday's environment.
Three Steps to Your TISAX Evidence Base
Capture Your IT Infrastructure
The Docusnap Enterprise Gateway (DEG) scans your environment agentlessly via WMI, SSH and SNMP. Servers, clients, network devices, Active Directory, virtualisation and cloud services flow automatically into the central CMDB. Credentials stay in the DEG and are never transmitted to the cloud.
Structure Risks and Measures
In the ISMS module you capture risks, vulnerabilities and threats and assign them to real assets from the CMDB. Every measure gets an owner, a status and a target date. The automatic CVE matching shows which known vulnerabilities actually affect your inventory.
Document Evidence and Policies
SmartDocs produce controlled documents with an approval workflow and full versioning. Who approved what, and when, is on record. The signed PDF export makes every document externally verifiable. Completed measures double as your compliance evidence.
Six Building Blocks for Your TISAX Assessment
Risk Management
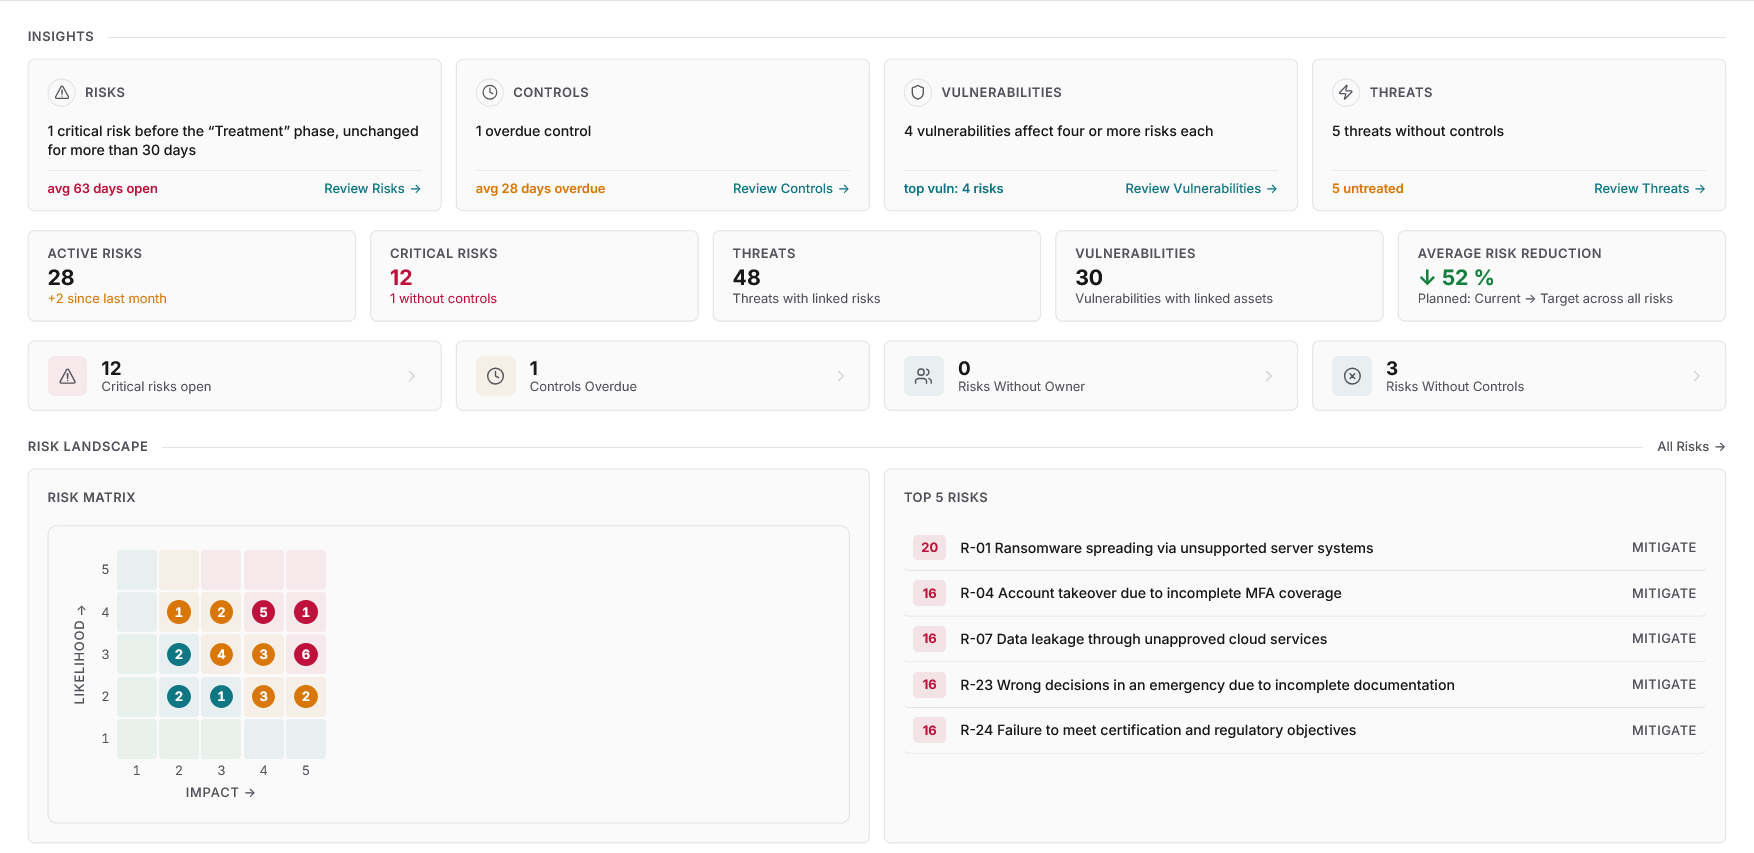
Risks are assigned to real assets from the CMDB. Risk matrices visualise likelihood and impact. You can track every measure from creation through implementation to effectiveness review.
Permission Analysis
Docusnap365 evaluates file, share and group permissions from two directions: by user and by resource. Nested groups and inherited rights become visible, graphically displayed and documented.
Automatic Inventory
More than 25 modules cover Windows, Linux, macOS, virtualisation, cloud services and network devices. The inventory updates with every scan, with no manual upkeep required.
Controlled Documents
SmartDocs deliver the document control ISO 27001 demands: approval workflow, major and minor versions, visual change comparison. No separate DMS required.
Vulnerability Management
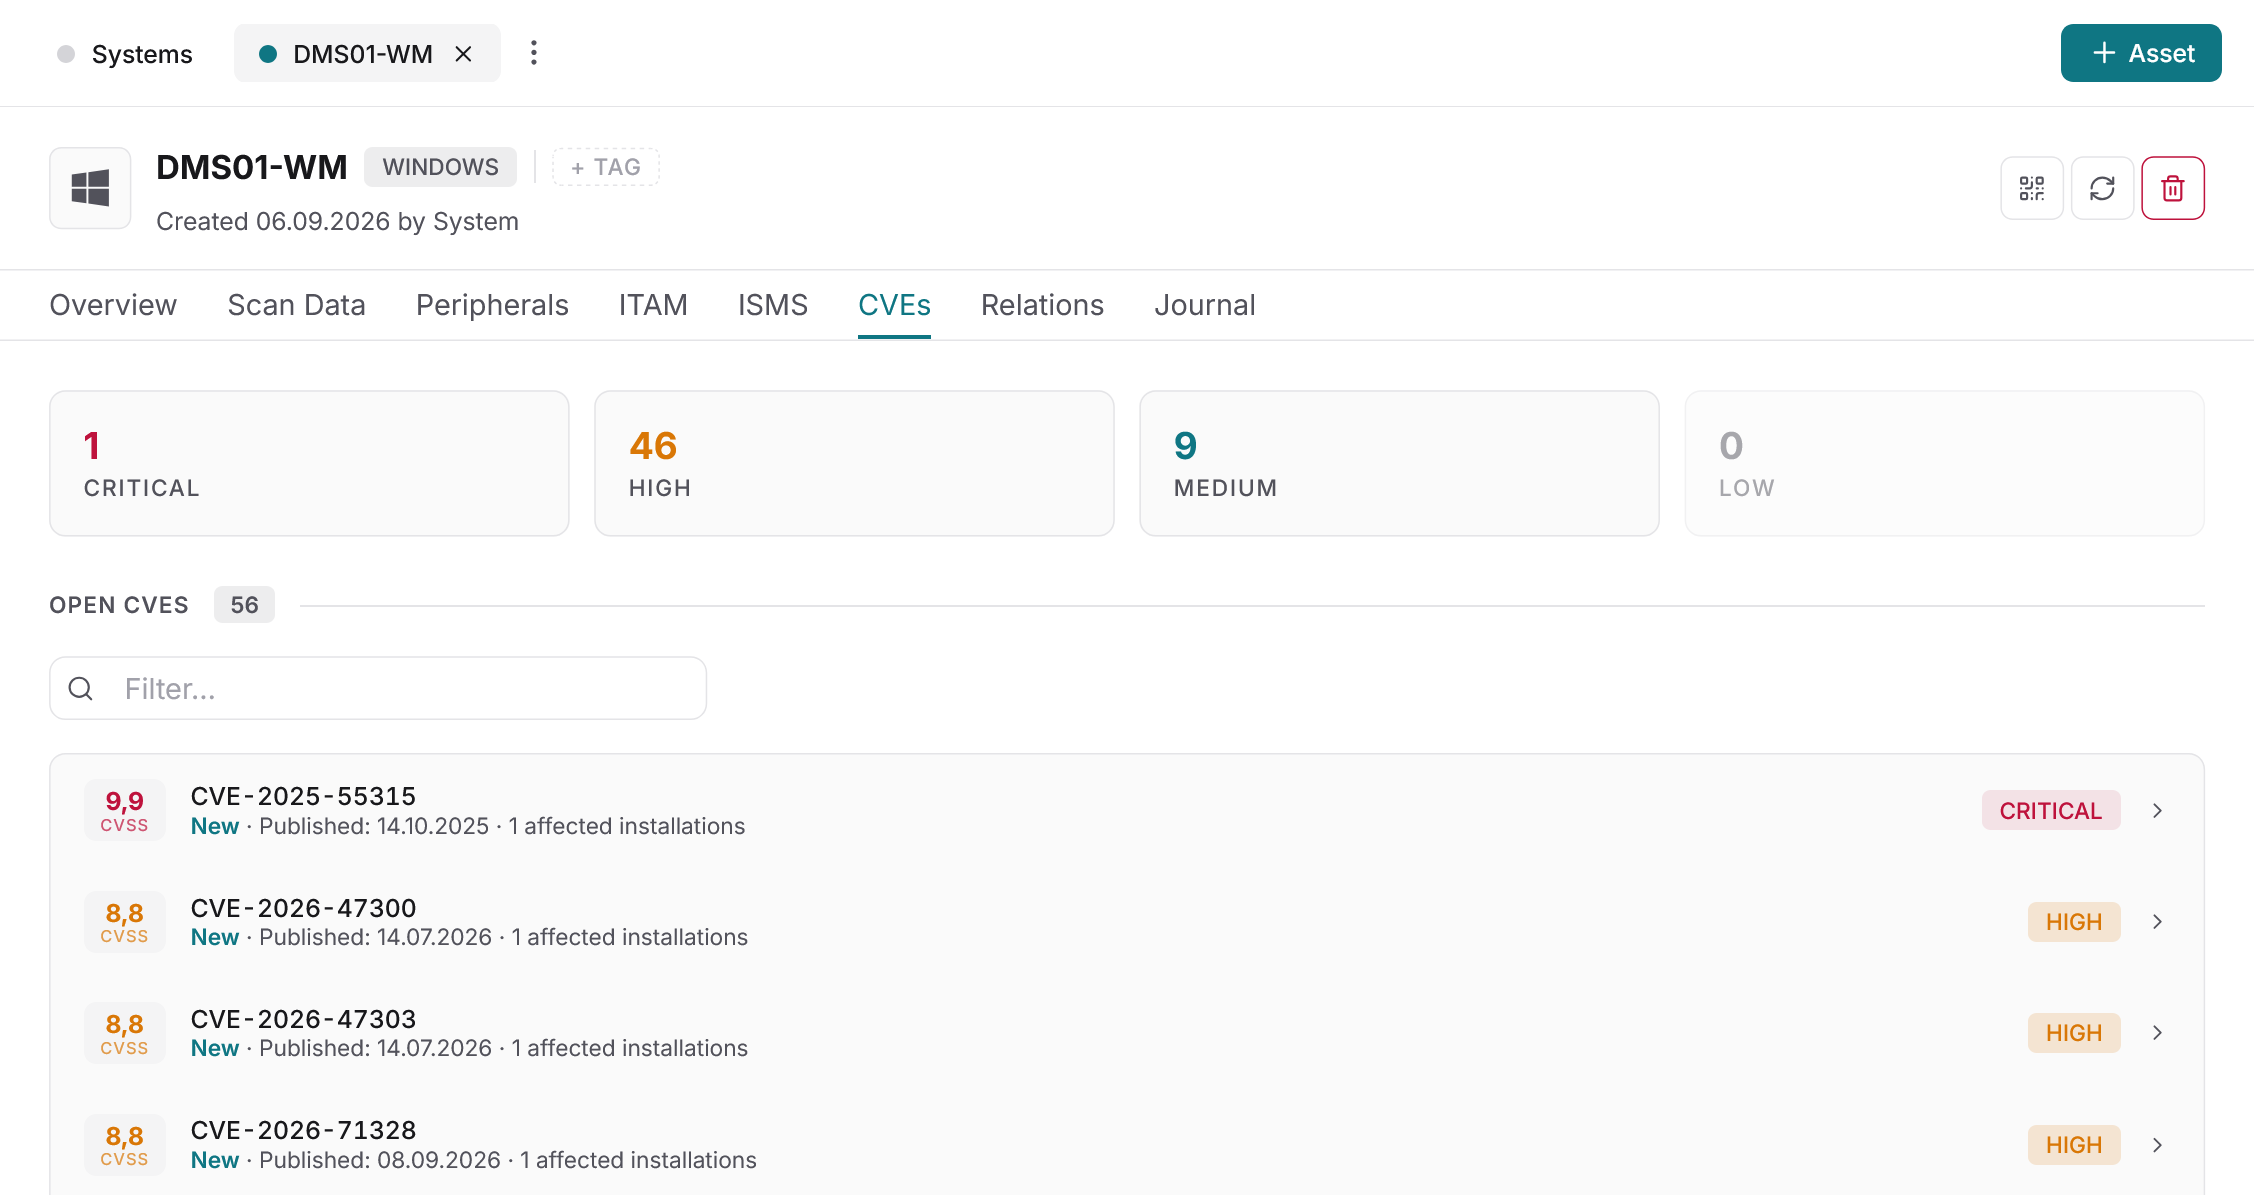
Automatic CVE matching against the inventoried estate. Only hits that affect actually installed software are shown. Deadlines, owners and decisions are documented.
Audit and Compliance Evidence
Built-in control catalogues for ISO 27001 and NIS-2. Controls can be assessed, cross-linked and connected to assets from the CMDB. Recurring reviews appear automatically as tasks.
One Data Foundation Instead of Five Isolated Tools
Many ISMS tools start with an empty form. You fill in fields, maintain lists, import data by hand. Docusnap365 works the other way round: the data foundation is built automatically by the inventory, and the ISMS operates on exactly that data.
Risks on Real Assets
No separate inventory, no double maintenance. Every risk is linked to a system that actually exists and whose configuration is documented. When an assessor asks, the answer is right where the risk is.
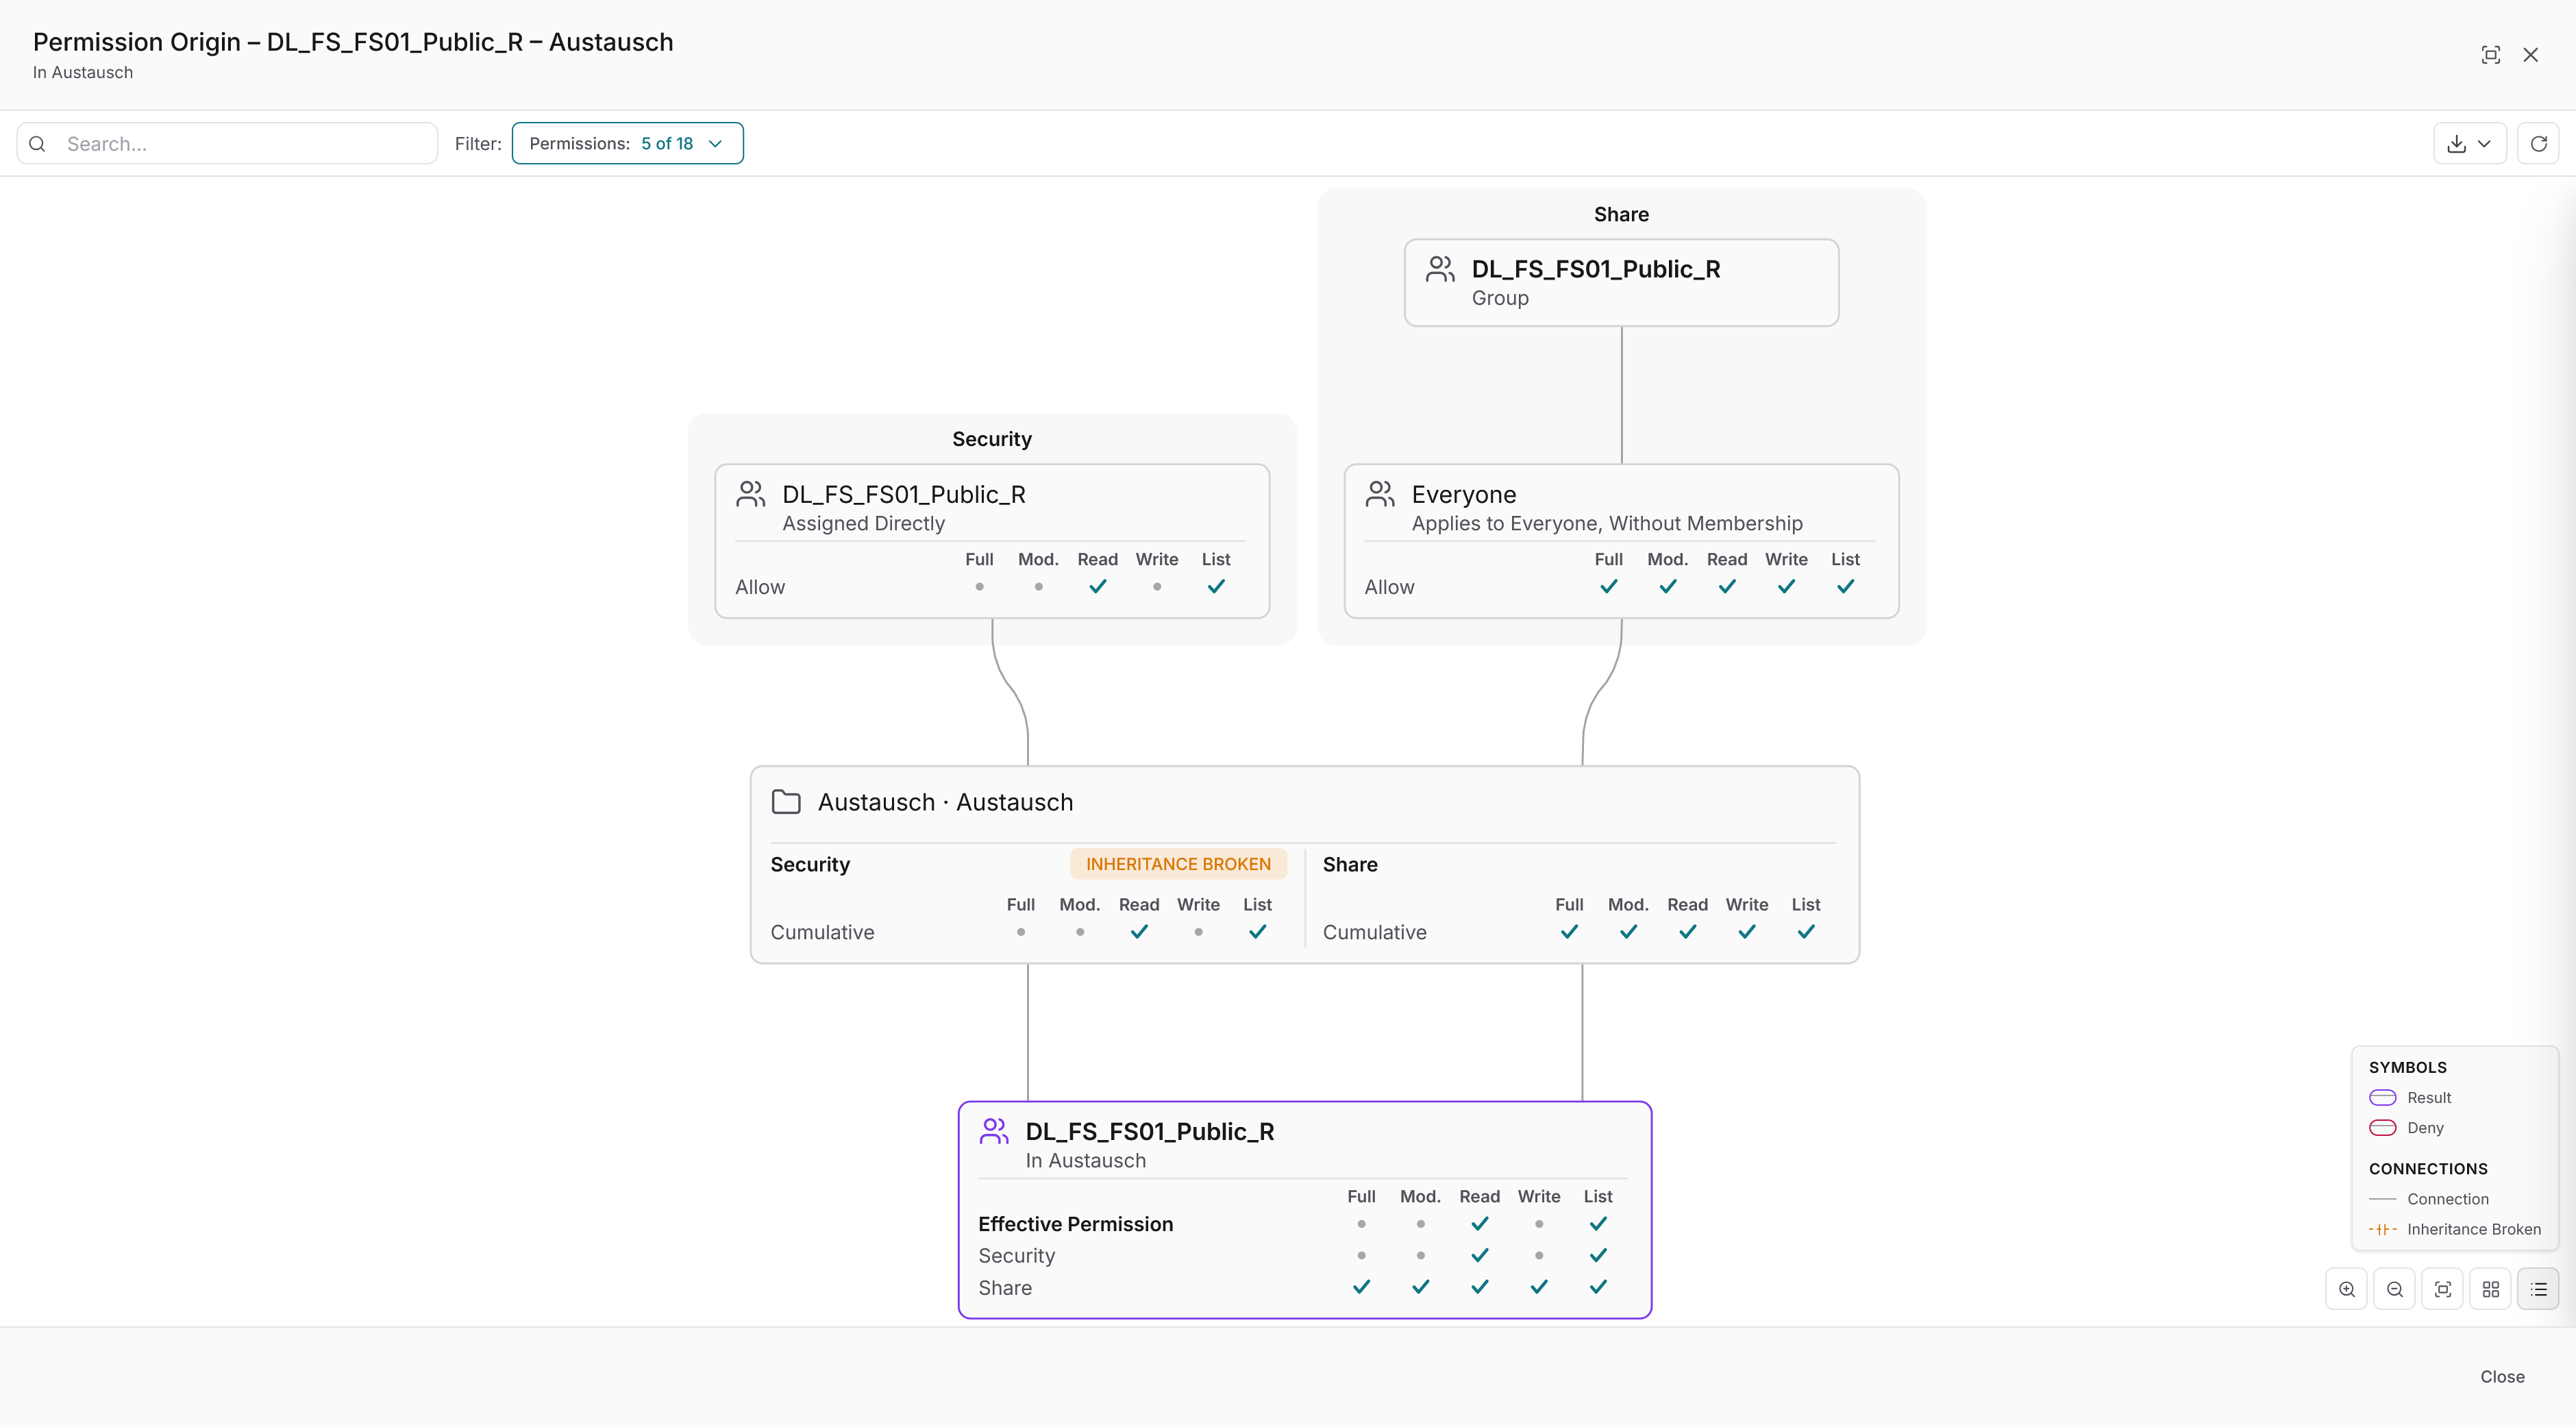
Access Rights Answered in Minutes
Who has access to which share? The permission analysis answers that question from two directions, including nested groups and inherited rights. A question that otherwise takes a lot of time is resolved with Docusnap365 in minutes.
Everything in One System
Inventory, risks, measures, policies, permissions and vulnerabilities sit in the same platform. No data reconciliation between separate tools, no export to another system just to get the full picture.
Docusnap365 as an IT Management Platform
The evidence base for TISAX is one use case of the platform. Docusnap365 covers additional areas your IT organisation needs in day-to-day operations.
IT Asset Management
Lifecycle, costs and warranty status for every asset: from procurement to decommissioning, with owners and period-accurate reporting.
AI Chat
Ask questions against your documentation, create assets, link risks: by chat, in natural language. The AI model runs in the EU, with no data shared with external providers.
Task Centre
All open measures, approvals and tasks from ISMS, ITAM and vulnerability analysis in a single view, with due dates and responsibilities.
Customising and Integrations
Custom fields, object types and saved queries. REST API and MCP interface for connecting to your existing systems.
Ask Your Documentation Instead of Searching It
In an assessment the questions come verbally and the answer has to be evidenced on the spot. The AI chat reads the data from inventory, ISMS and permission analysis and answers in natural language.
Nine systems are recorded as carriers of design data: two PDM servers, one file server cluster and six CAD workstations. All nine are linked to the risk “Loss of confidential development data”.
24 accounts across five groups, two of them nested. Three accounts hold full control, one belongs to a former employee.
Six measures have passed their target date, four of them tied to risks with high impact. Three owners in IT operations are responsible.
31 hits on actually installed software, eight of them rated critical. 14 clients and two application servers are affected.
Three SmartDocs are in the approval workflow, among them the access control policy. The oldest approval has been with its owner for 19 days.
Frequently Asked Questions About TISAX and Docusnap365
Is Docusnap365 a certified TISAX tool?
Which TISAX-relevant areas does the software cover?
How does the automatic inventory work?
Can I create policies and security concepts directly in Docusnap365?
How are risks assigned to actual IT systems?
Where is the data hosted, and what about data privacy?
Prepare Your TISAX Assessment With Structure
Docusnap365 provides the data foundation, the structure and the evidence. Explore the platform and start building the evidence base for your assessment.