Platform
Always audit-ready instead of last-minute sprints
ISO/IEC 27001 is preloaded. For NIS2 in Germany and Austria and for GDPR, Docusnap comes with its own frameworks. You always see where you stand and what evidence is still missing.
Ready to use with pre-loaded frameworks
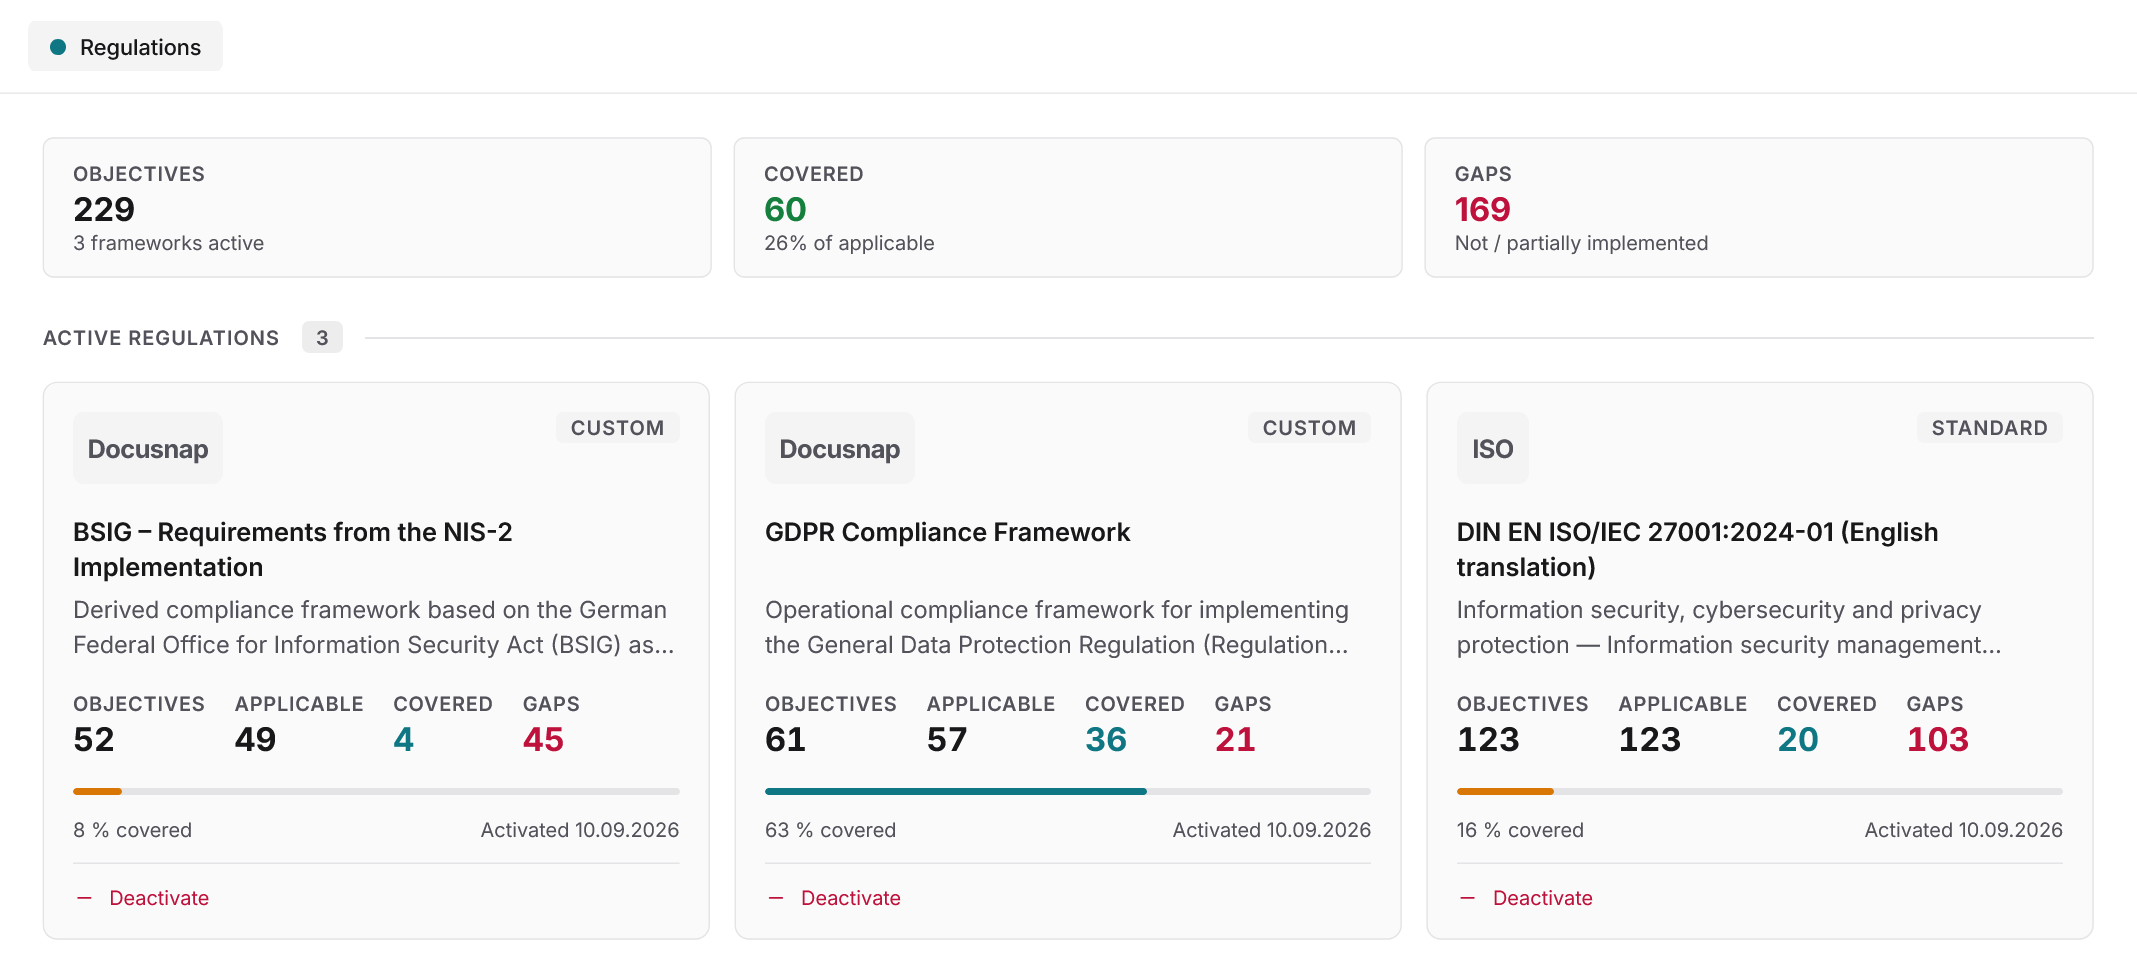
Compliance foundation
Frameworks, controls and completeness in one place
Docusnap starts with the ISO 27001 standard and the BSI Cloud Computing Compliance Criteria Catalogue (C5). We built the compliance frameworks for NIS2 and GDPR ourselves, so you don’t start from scratch. For NIS2, you get one framework for Germany (BSI Act, BSIG) and one for Austria (NISG). You assess each control individually, link controls to one another and connect them to measures, documents and assets, so it stays visible how a measure contributes to a control and which systems it affects. The completeness overview shows where evidence exists and where gaps remain.
Pre-loaded frameworks
ISO 27001, the BSI cloud catalog (C5) and our own frameworks for NIS2 (DE, AT) and GDPR are included. You start with the assessment right away.
Assess and link controls
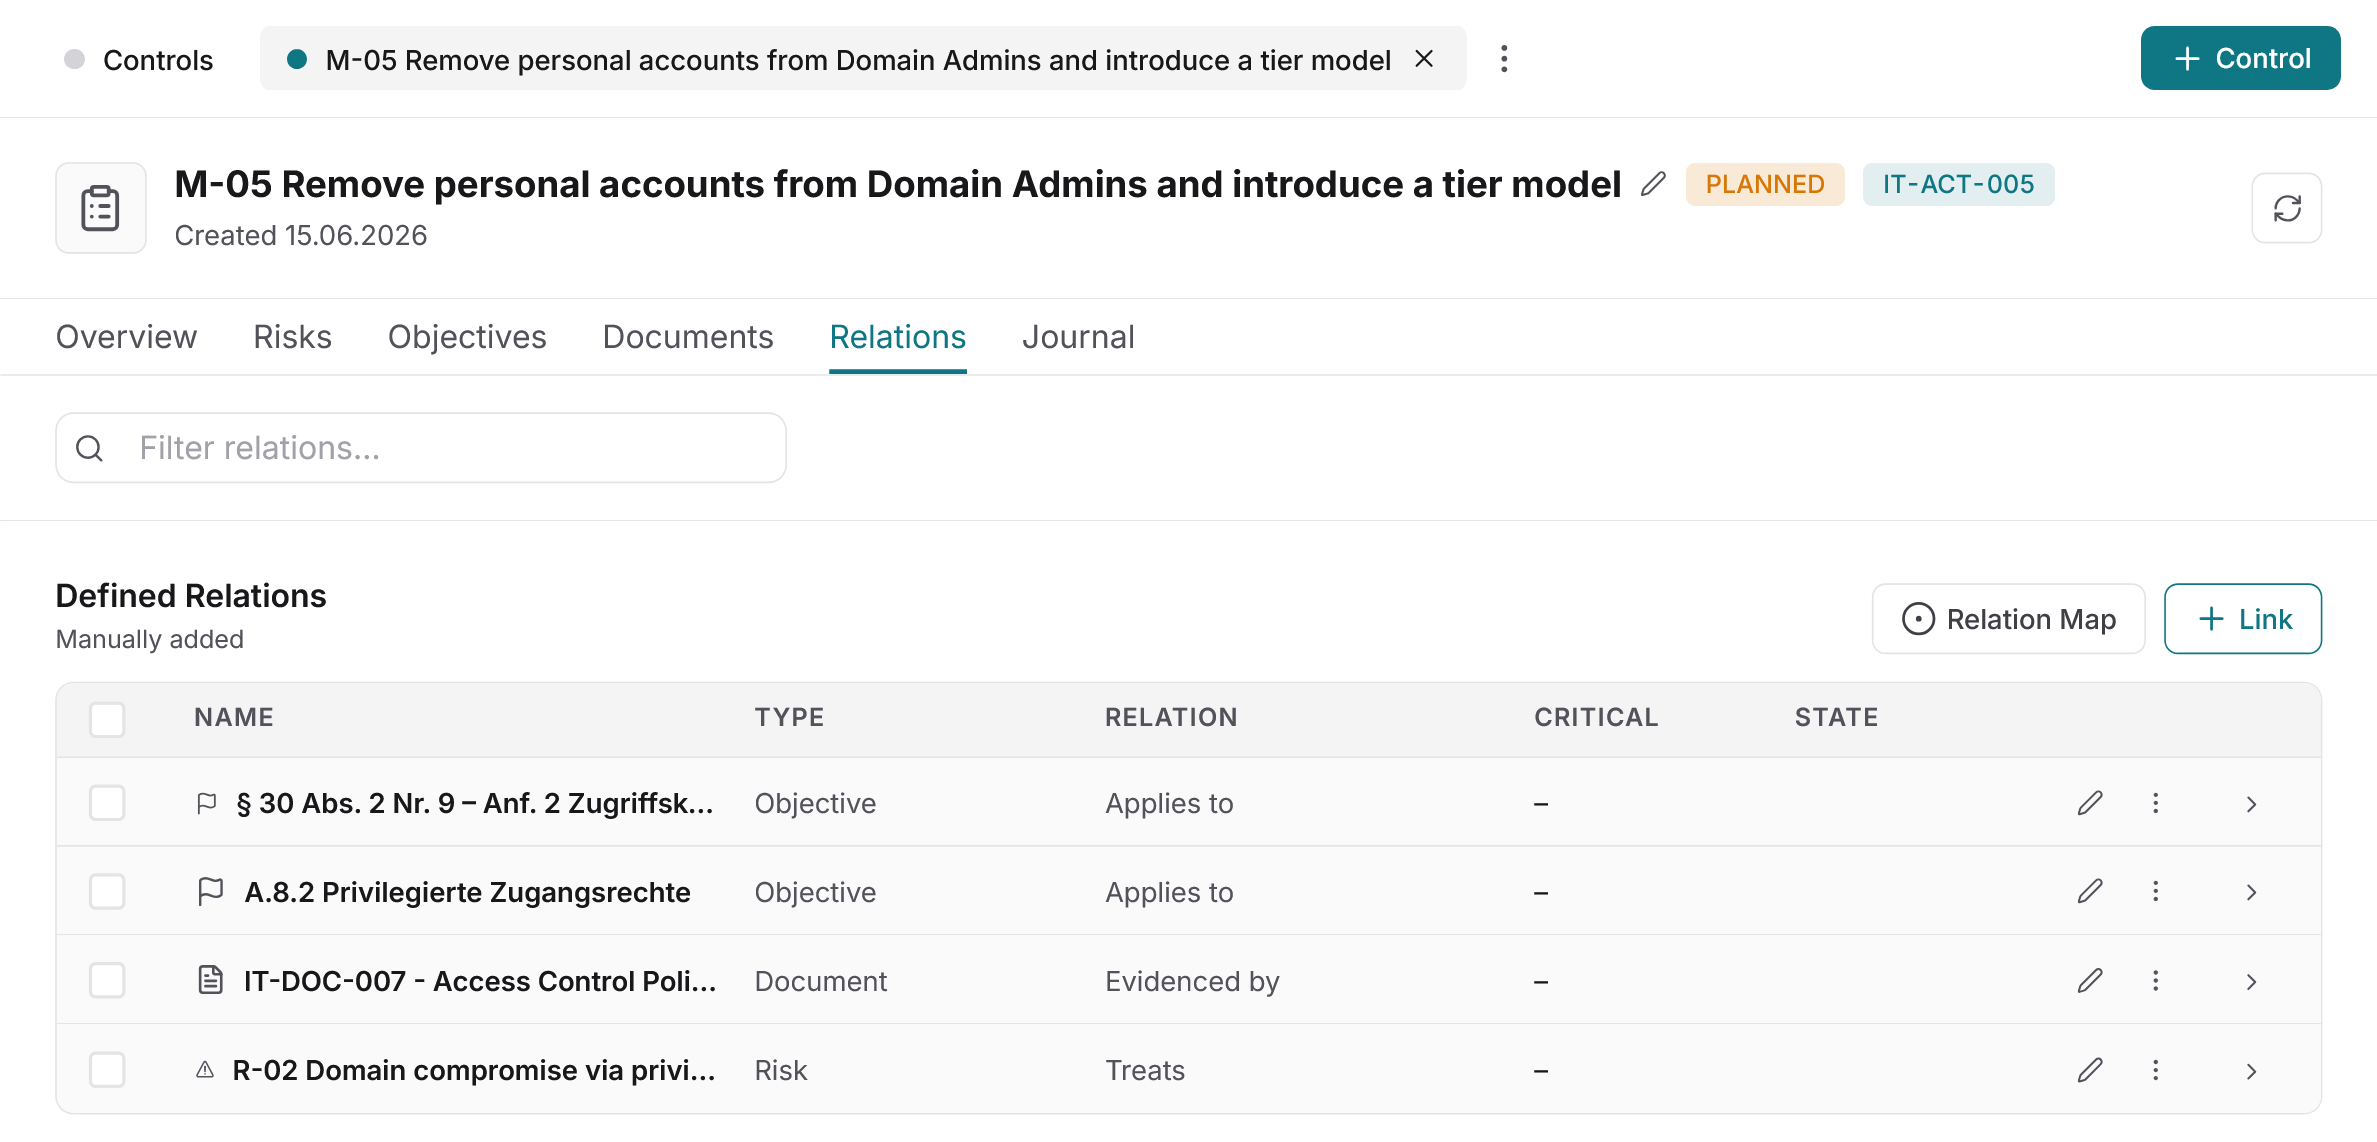
Each control is assessed individually. Links between controls make visible which measure contributes to ISO 27001 and NIS2 at the same time.
Completeness at a glance
The completeness overview continuously shows where evidence exists and where gaps remain. No scrambling before the audit date.
Frameworks are in place, controls are ready for your assessment.
Try nowAI support
Ask instead of reading reports
AI-powered analysis supports you in assessing controls and analysing your ISMS status. Ask questions about your documented controls and evidence instead of working through reports.
Daily operations
From setup to day-to-day
An ISMS does not run on the initial assessment alone. What matters in practice is whether reviews recur reliably, exceptions are properly documented and changes remain traceable.
Applicability and exceptions
Non-applicable controls are documented with a stated reason, not silently skipped. That is the first question in any audit.
Recurring measures
Annual reviews and periodic evidence requirements appear automatically as tasks. They do not need to be remembered.
Reviews with deadlines and owners
Every control has a review date and an assigned person. No shared responsibility, no forgotten deadlines.
Relationships and change history
Controls, measures, documents and assets are interlinked. Every change is recorded in the journal. In an audit, the path matters as much as the current state.
Platform
Compliance on real systems
The ISMS module runs on the same platform as the CMDB, permission analysis and controlled SmartDocs. Controls are attached to real assets, not to a separate description of the target state.
CMDB
Controls and measures are linked to real IT systems documented in the CMDB. Compliance evidence is based on the actual state of the infrastructure.
Controlled SmartDocs
Policies and procedures are maintained as controlled documents, versioned and approved. For every document, it is traceable who changed it and when.
Permission analysis
Permission analysis shows who can access which systems and data. For access management controls under ISO 27001, a reliable basis instead of manual surveys.
Frequently asked questions about the ISMS module in Docusnap
Which laws and standards are preloaded in Docusnap?
Does Docusnap support GDPR implementation?
How does Docusnap show where evidence is missing?
How does the link between controls and assets work?
What happens when a control is not applicable?
How does AI support ISMS work?
How are recurring reviews managed?
Does Docusnap support NIS2 in Austria as well?
Are these official standards?
What effort does Docusnap take off my plate?
Start ISMS
Start with the ISMS that already knows your IT landscape
Standards and frameworks are preloaded, controls are waiting for your assessment.